Lucid✓ Verified

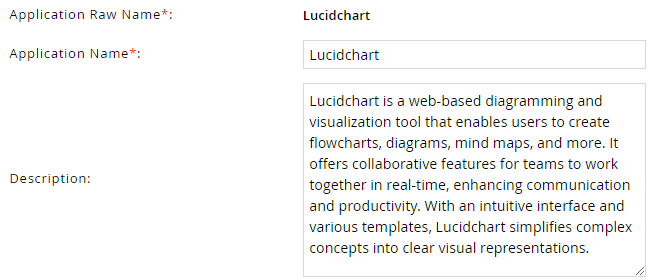
 Lucidchart is a web-based diagramming and visualization tool that enables users to create flowcharts, diagrams, mind maps, and more. It offers collaborative features for teams to work together in real-time, enhancing communication and productivity. With an intuitive interface and various templates, Lucidchart simplifies complex concepts into clear visual representations. Identities ❌ | Accounts ✔️ | Groups ❌ | App Roles ✔️ | Entitlements ❌ |
Application
Steps
- Login to RSA G&L console as System Administrator.
- Navigate to Resources > Application.
- Click on Create Application and select Other Application.
- Enter the details as shown below.
- Click Finish.
Account Collector
This section explains the process for configuring an account collector for the Lucid application. We will use the RSA G&L Generic REST collector 1 for this purpose.
Steps
- Login to RSA G&L console as System Administrator.
- Navigate to Resources > Applications.
- Click on Lucid.
- Navigate to Collectors tab and click on Create Account Collector. Enter the details as shown below.

- Click Next and enter the connection details..

💡 Info: Lucid only supports OAuth authentication type. Refer to OAuth2 for more information. - Click Next. Select the data types that the collector will be collecting from Lucid

- Click Next. On the Account Data page, enter the following configurations.
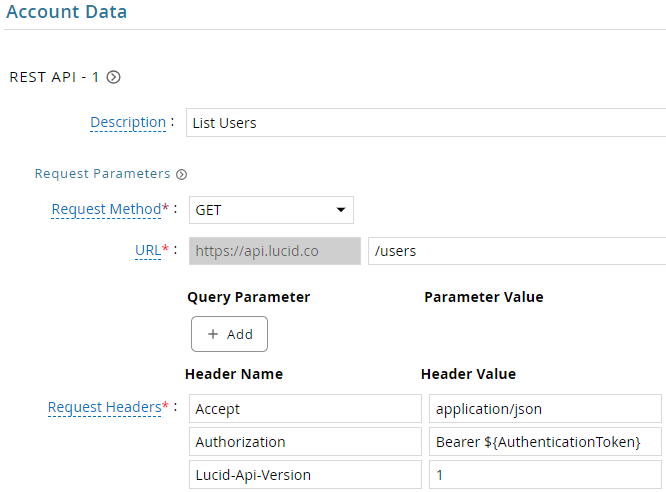
| Request | |
| Method | GET |
| URL | /users |
| Request Headers | |
| Accept | application/json |
| Authorization | Bearer ${AuthenticationToken} |
| Lucid-Api-Version | 1 |
| Response Mappings | |
| AccountId | $.*.email |
| Id | $.*.userId |
| UserName | $.*.username |
- Click Next. In the Map Collector Attributes to Account Attributes, map the collected account attributes.
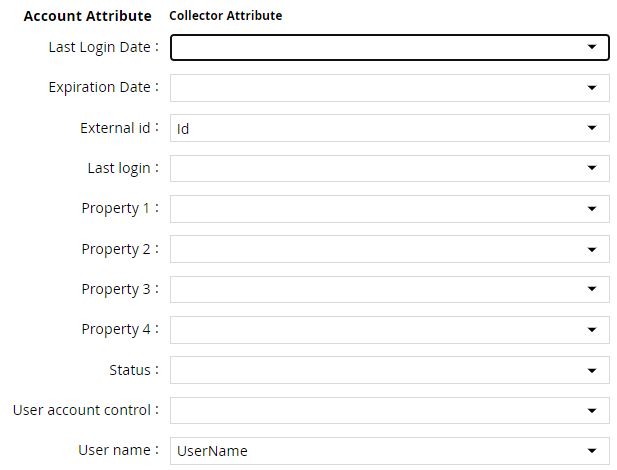
- Click Next. In the Map Collector Attributes to Account Mapping Attributes, map the user reference attribute.

- Click Next. In the User Resolution Rules, map the user to account.

- Click Finish. Use the
Testfunction to make sure the configurations are accurate.
Entitlement Collector
This section explains the process for configuring an entitlement collector to collect site roles and assignments from the Lucidchart application. We will use the RSA G&L Generic REST collector for this purpose.
Since Lucid does not provide an API for listing admin roles, we will use a custom web service for the EDC. Refer to Custom Web Service : Admin Roles for more information.
Steps
- Login to RSA G&L console as AveksaAdmin.
- Navigate to Resources > Applications.
- Click on Lucid.
- Navigate to Collectors tab and click on Create Entitlement Collector. Enter the details as shown below.

- Click Next and enter the connection details as shown in Step 5 of Account Collector. 💡 Note that the Use Base URL for all API(s) will be unchecked.
- Click Next. Select the data types that the collector will be collecting from Lucid.

- Click Next. On the App Role Data page, enter the following configurations.
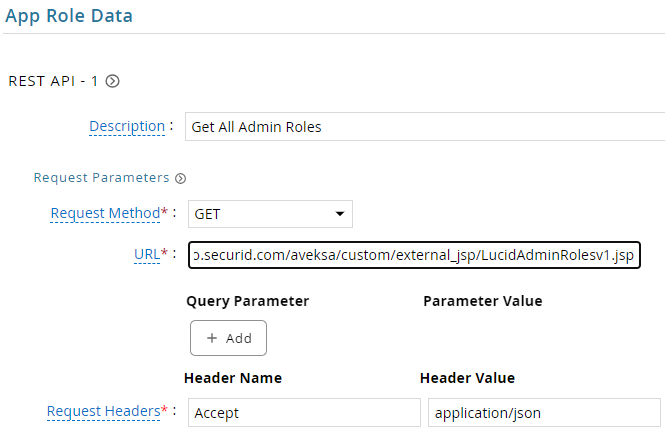
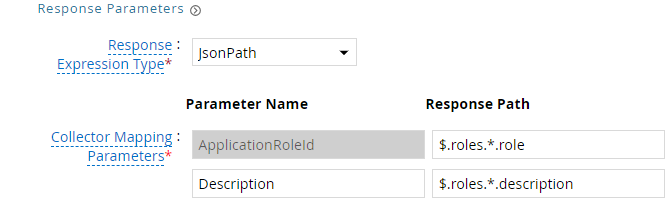
| Request | |
| Method | GET |
| URL | https://instance.securid.com/aveksa/custom/external_jsp/LucidAdminRolesv1.jsp |
| Request Headers | |
| Accept | application/json |
| Response Mappings | |
| ApplicationRoleId | $.roles.*.role |
| Description | $.roles.*.description |
- Click Next. On the App-Role Account Membership collection page, enter the following configurations.
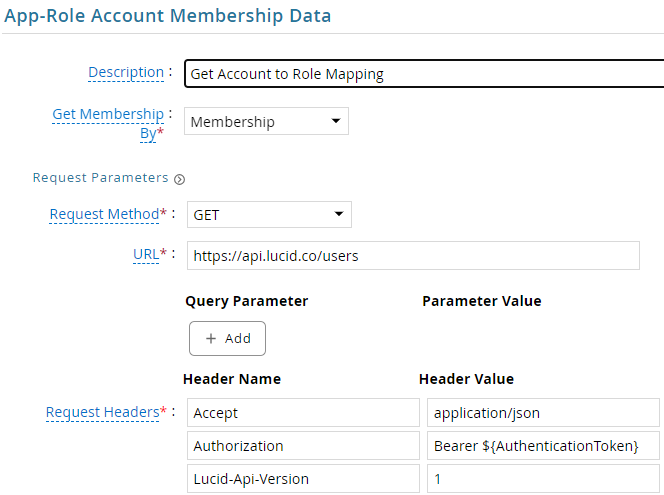
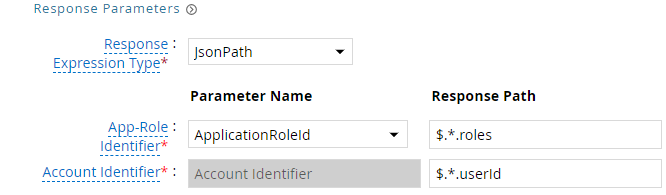
| Request | |
| Method | GET |
| URL | https://api.lucid.co/users |
| Request Headers | |
| Accept | application/json |
| Authorization | Bearer ${AuthenticationToken} |
| Lucid-Api-Version | 1 |
| Response Mappings | |
| Application Role Id | $.*.roles |
| Account Identifier | $.*.userId |
- Click Next. In the Map Collector Attributes to App Role Attributes, map the collected account attributes.

- Click Next. In the Account Evaluation, map the account collector to account value.

- Click Next and then click Finish. Use the
Testfunction to make sure the configurations are accurate.
Application Setup
This section explains the process of setting up Lucid for integration with G&L.
Steps
- Login to Lucid Developer Console, https://admin.lucid.app/developer. You need to have Developer Tools enabled by the Lucid admin for your organization.
- Click on New Application.
- Provide a suitable name and click Create.

- Click on OAuth 2.0 tab.
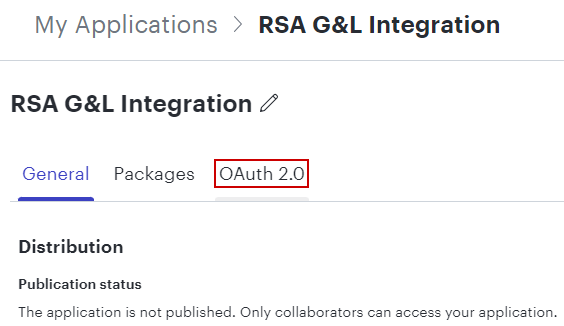
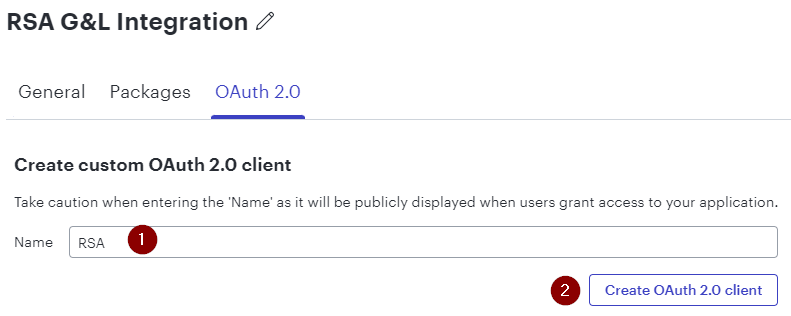
- Provide a client name and click Create OAuth 2.0 client.
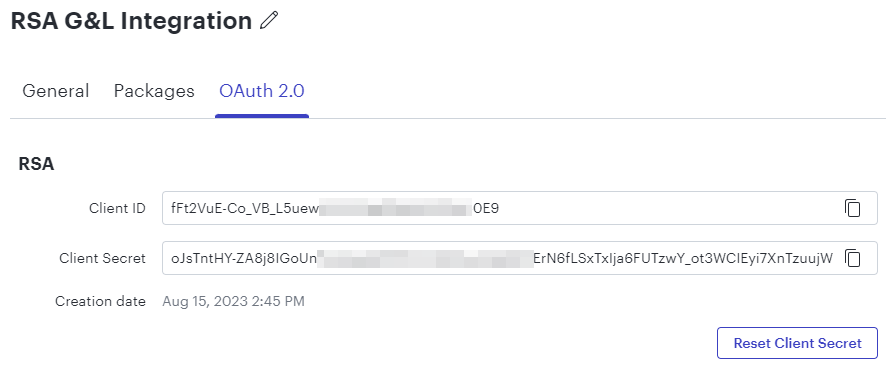
- Copy the client id and client secret.
- Click on Add Redirect URI and add the G&L OAuth call back URL https://instance.securid.com/aveksa/oauth/callback.

Authentication
OAuth2
This section explains the process of setting up RSA G&L ADC with OAuth2 authentication.
Steps
- Login to RSA G&L console as System Administrator.
- Create or Edit a generic REST ADC that will be using OAuth2 authentication.
- On the Connection Details page, configure the following.
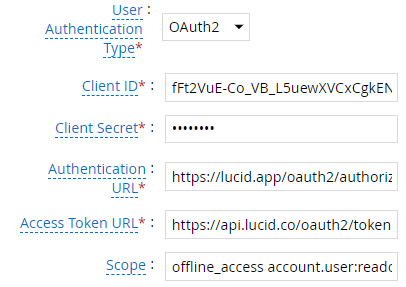
| Request | |
| Client ID | - |
| Client Secret | - |
| Authentication URL | https://lucid.app/oauth2/authorizeAccount |
| Access Token URL | https://api.lucid.co/oauth2/token |
| Scope | offline_access account.user:readonly |
- Click on Get OAuth 2.0 Access Token.
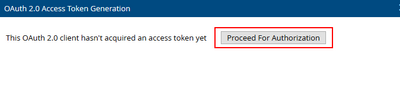
- Click on Proceed For Authorization.
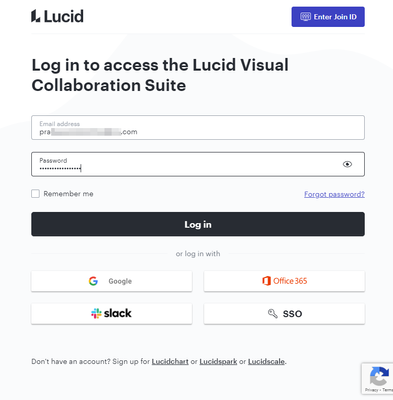
- Login to Lucid account.
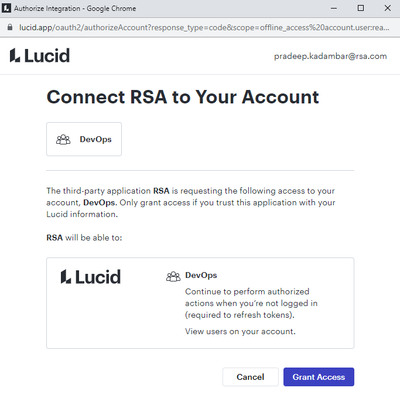
- The below message indicates that RSA G&L has successfully acquired a token.
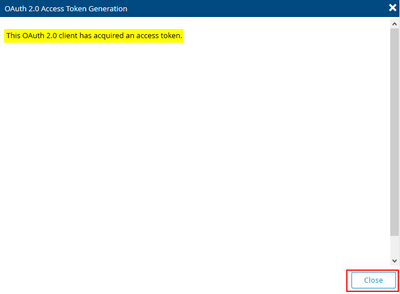
- Click Close.
- Save the collector configuration. Use the
Testfunction to make sure the configurations are accurate
Custom Web Service
Admin Roles
Since Lucid does not provide an API for listing admin roles, we will use a custom JSP that will publish the admin roles.
Steps
- Open a text editor and save the contents below as
LucidAdminRolesv1.jsp.
<%@ page language="java" contentType="application/json" %>
<%
    String jsonData = "{"
        + "\"roles\": ["
        + "{\"role\":\"billing-admin\",\"description\":\"Billing admins can change payment options for the account.\"},"
        + "{\"role\":\"document-approver\",\"description\":\"Document approvers can approve documents.\"},"
        + "{\"role\":\"team-admin\",\"description\":\"Team admins can access and edit team settings, including user roles and groups.\"}"
        + "]"
        + "}";
%>

<%
    response.setContentType("application/json");
    out.print(jsonData);
%>
- Login to RSA G&L console as AveksaAdmin.
- Navigate to Admin > User Interface.
- Click on Files.
- Select External JSP Pages and click on Upload.
- Select the
LucidAdminRolesv1.jspand click OK. - Verify by accessing this URL in the browser https://instance.securid.com/aveksa/custom/external_jsp/LucidAdminRolesv1.jsp
References
- Lucid REST API
- Authentication
- Obtaining an Access Token
- Users
- List Users
- OAuth 2.0 Authorization Code Grant (RFC 6749)
COL010